


Get all the Information About CyberArk PAM-DEF Exam 2023 Practice Test Questions
Check Real CyberArk PAM-DEF Exam Question for Free (2023)
CyberArk PAM-DEF exam covers a wide range of topics, including CyberArk Defender, PAM, and privileged access management policies. It also covers the best practices for implementing and managing PAM security solutions. PAM-DEF exam is designed to test the ability of the candidates to assess their organization's security posture, identify vulnerabilities, and implement appropriate security measures to mitigate risks.
CyberArk Defender - PAM certification exam is a comprehensive test that covers a variety of topics related to privileged access management. It is designed to validate the skills and knowledge of professionals who work with CyberArk's PAM solutions, and is a valuable credential for those looking to advance their careers in the field of security or system administration. Candidates can prepare for the exam by gaining experience with CyberArk's PAM solutions and by studying the exam objectives and materials provided by CyberArk.
CyberArk PAM-DEF exam is an essential certification for cybersecurity professionals who want to specialize in PAM security solutions and CyberArk Defender. It is a challenging exam that requires a deep understanding of the topics covered, including CyberArk Defender, PAM, and privileged access management policies. By passing PAM-DEF exam, cybersecurity professionals can demonstrate their expertise and enhance their career prospects in the field of cybersecurity.
NEW QUESTION # 50
Which of the following are secure options for storing the contents of the Operator CD, while still allowing the contents to be accessible upon a planned Vault restart? (Choose three.)
- A. Store the CD in a physical safe and mount the CD every time Vault maintenance is performed
- B. Copy the entire contents of the CD to the system Safe on the Vault
- C. Store the server key in a Hardware Security Module (HSM) and copy the rest the keys from the CD to a folder on the Vault Server and secure it with NTFS permissions
- D. Copy the entire contents of the CD to a folder on the Vault Server and secure it with NTFS permissions
Answer: A,C,D
NEW QUESTION # 51
What is the purpose of the password change process?
- A. To test that CyberArk is storing accurate credentials for accounts
- B. To allow CyberArk to manage unknown or lost credentials
- C. To change the password of an account according to organizationally defined password rules
- D. To generate a new complex password
Answer: C
NEW QUESTION # 52
Platform settings are applied to _________.
- A. Individual Accounts
- B. The entire vault.
- C. Safes
- D. Network Areas
Answer: C
NEW QUESTION # 53
A newly created platform allows users to access a Linux endpoint. When users click to connect, nothing happens.
Which piece of the platform is missing?
- A. UnixPrompts.ini
- B. UnixProcess.ini
- C. PSM-RDP Connection Component
- D. PSM-SSH Connection Component
Answer: D
NEW QUESTION # 54
Within the Vault each password is encrypted by:
- A. its own unique key
- B. the recovery private key
- C. the recovery public key
- D. the server key
Answer: A
NEW QUESTION # 55
Accounts Discovery allows secure connections to domain controllers.
- A. FALSE
- B. TRUE
Answer: A
NEW QUESTION # 56
Match the log file name with the CyberArk Component that generates the log.
Answer:
Explanation:

NEW QUESTION # 57
A newly created platform allows users to access a Linux endpoint. When users click to connect, nothing happens.
Which piece of the platform is missing?
- A. UnixPrompts.ini
- B. UnixProcess.ini
- C. PSM-RDP Connection Component
- D. PSM-SSH Connection Component
Answer: C
NEW QUESTION # 58
Which Automatic Remediation is configurable for a PTA detection of a "Suspected Credential Theft"?
- A. Rotate Credentials
- B. Reconcile Credentials
- C. Add to Pending
- D. Disable Account
Answer: B
NEW QUESTION # 59
Which parameter controls how often the CPM looks for accounts that need to be changed from recently completed Dual control requests.
- A. The CPM does not change the password under this circumstance
- B. ImmediateInterval
- C. Interval
- D. HeadStartInterval
Answer: C
NEW QUESTION # 60
Which of the following properties are mandatory when adding accounts from a file? (Choose three.)
- A. Hostname
- B. All required properties specified in the Platform
- C. Username
- D. Address
- E. Safe Name
- F. Platform ID
Answer: B,E,F
NEW QUESTION # 61
Match each PTA alert category with the PTA sensors that collect the data for it.
Answer:
Explanation: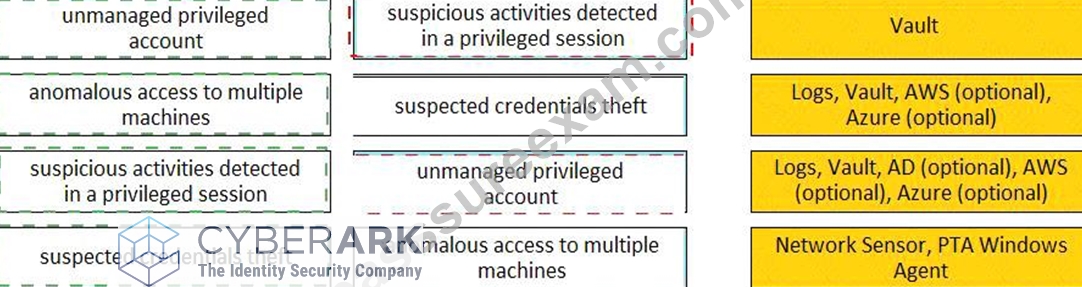

NEW QUESTION # 62
It is possible to control the hours of the day during which a user may log into the vault.
- A. TRUE
- B. FALSE
Answer: A
NEW QUESTION # 63
In order to connect to a target device through PSM, the account credentials used for the connection must be stored in the vault?
- A. False. Because if credentials are not stored in the vault, the PSM will prompt for credentials.
- B. False. Because if credentials are not stored in the vault, the PSM will log into the target device as PSM Connect.
- C. True.
- D. False. Because the user can also enter credentials manually using Secure Connect.
Answer: D
NEW QUESTION # 64
To manage automated onboarding rules, a CyberArk user must be a member of which group?
- A. CPM User
- B. Vault Admins
- C. Auditors
- D. Administrators
Answer: B
NEW QUESTION # 65
Which utilities could you use to change debugging levels on the vault without having to restart the vault.
Select all that apply.
- A. PrivateArk Server Central Administration
- B. Edit DBParm.ini in a text editor.
- C. PAR Agent
- D. Setup.exe
Answer: A,C
Explanation:
Explanation
PAR-Private Ark Remote Control Agent allows you to perform several Vault admin tasks (without restarting the Vault) and view machine statistics.
NEW QUESTION # 66
The Password upload utility can be used to create safes.
- A. FALS
- B. TRUE
Answer: B
NEW QUESTION # 67
tsparm.ini is the main configuration file for the Vault.
- A. True
- B. False
Answer: B
NEW QUESTION # 68
If a user is a member of more than one group that has authorizations on a safe, by default that user is granted________.
- A. the vault will not allow this situation to occur.
- B. the cumulative permissions of all groups to which that user belongs.
- C. only those permissions that exist on the group added to the safe first.
- D. only those permissions that exist in all groups to which the user belongs.
Answer: B
NEW QUESTION # 69
......
Use Free PAM-DEF Exam Questions that Stimulates Actual EXAM : https://www.passsureexam.com/PAM-DEF-pass4sure-exam-dumps.html
Get Ready to Boost your Prepare for your PAM-DEF Exam with 180 Questions: https://drive.google.com/open?id=1GL3KEMqzjXl_d1Q05Z0_vCv2zMvH3_vA